Authorizer
Authorizer is a Password Manager for Android. It emulates an HID keyboard over USB and enters your credentials on your target device. Additionally it supports OTP :key::mobile_phone_off:
- Readme
- Issues
Authorizer
A Password Manager for Android with Auto-Type over USB and Bluetooth, OTP and much more.
The idea behind Authorizer is, to use old smartphones as a hardware password manager only. To avoid manual typing of long and complex passwords everytime you need them, Authorizer provides Auto-Type features over USB and Bluetooth. It pretends to be a keyboard (e.g. over an USB On-The-Go adapter) and with a button press inside the app, it will automatically type the password for you on your pc, laptop, tablet or other smartphone.

Authorizer is based on PasswdSafe a Password Safe port for Android and FreeOTP.
Features
- Auto-Type over USB
- Auto-Type over Bluetooth (experimental)
- Different keyboard languages (HID Usage Tables)
- English (US)
- English (GB)
- German
- German (Apple)
- German (CH)
- French (CH)
- Neo 2 (Layer 1,2 and 3)
Features in Detail
Auto-Type over USB and Bluetooth
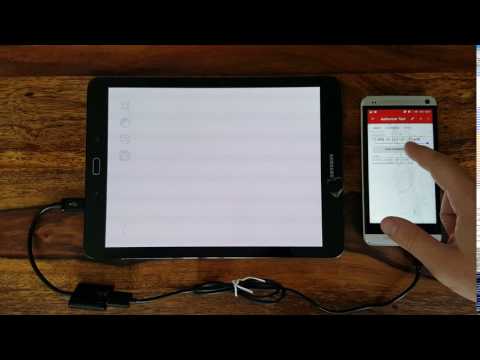 Authorizer is able to pretend to be an HID Keyboard so it can auto-type the credentials over USB and Bluetooth.
There are Auto-Type buttons at the password entry view. If a button is pressed longer, a different keyboard layout can be choosen. Additional, there is a USB Quick Auto-Type button in the TreeView which auto-types the respective password on a long press.
There are different settings per password entry like delimiter and the password return suffix. In the general App preferences a default keyboard layout can be choosen.Auto-Type over USB requires support of the USB HID device role. This can be enabled with my USB Gadget Tool.
Auto-Type over Bluetooth is currently an experimental feature and only available on Android Pie (9.0) or higher.
Asymmetric encrypted backup on USB mass storage
The concept behind Authorizer is to have an offline device. As a consequence, it can’t create password file backups over the network. To create backups in a comfortable way, Authorizer will open a backup dialog if it detects a new connected mass-storage (e.g. an USB stick connected over an USB On-The-Go adapter). By pressing «Backup now» in this dialog, a backup folder can be selected. It must contain a GPG public key with the file name «pubkey.asc». The default password file will be encrypted with this GPG key and stored in the selected folder.
This feature can be enabled over the general App preference «Enable GPG backup on USB storage».OTP integration
Besides standard username & password entries, Authorizer also supports two-factor authentication (2FA) over one-time passwords (OTP). Time-based (TOTP) and HMAC-based (HOTP) one-time passwords are supported.
The OTP secret can be added to a password entry manually or by scanning a QR code. Afterwards, a press on the empty token field («——«) will generate a new OTP. It is also possible, to auto-type the OTP over USB or Bluetooth by addingas a placeholder directly in the username or password, e.g. in the password «myPa$sword » will be replaced with a newly generated OTP.
Like username, password and other data, the OTP secret is stored in the password file.Additional Auto-Type placeholders
In addition to the
placeholder, Authorizer also supports and for the tabulator and return key. Adding these to the username and/or password will result in auto-typing the respective key (tab or return) instead of the placeholder.
Example: if «peter» is set as the username, «peter» followed by the tabulator key and a newly generated OTP will be auto-typed. Roadmap
- NFC support
- Smartcard emulation (e.g. OpenPGP cards, etc.)
- CTAP + CTAP2 integration for U2F and WebAuthn
- Redesign of the App
- Refactoring the HID Keyboard Layout code
Requirements
- For Auto-Type over USB: USB Gadget Tool or an Android Kernel compiled with Android Keyboard Gadget is required
- For Auto-Type over Bluetooth: Android Pie or higher is required. Tested devices:
- Samsung Galaxy S8: WORKING
- HTC One M8 (LineageOS 16.0): WORKING
Contributions & Community
Contributions are highly welcome.
For support & development discussions around Authorizer, feel free to contact me.Proof of Concept
Proof-of-Concept app for Auto-Typing (USB Keyboard emulation): Authorizer-PoC
Loved By Users
Join our community on Discord. You can also share your experience here and help us build more trust.
“ First time I found Authorizer at Product Hunt I fall in love with this. Then I realize this is a perfect fit solution for me. So, I want to say thank you for building an amazing product. Especially as you made it Open Source. ”
“ Authorizer simplifies the implementation of a login system and is fast and light on resources. The React.js library also vastly simplifies the implementation of state management in a project. The author, Lakhan Samani, is also extremely helpful and easy to work with. Overall, Authorizer saves numerous hours of headaches and provides a great experience for developers. ”
“ I have been working on an edutainment product for the past few months. The authentication, authorization flow was one of the tasks that I had to take care of. I used the Authorizer for the same and it did not take me much time, from integration with the product to setting it up on the cloud. It was a great experience as a developer to be able to use an open-source solution to a fairly complex problem with such ease. Thanks to the authorizer team. ”
“ Authorization/Authentication has been always big pain but I found Authorizer is the simplest and fastest way of building auth service for our app. I also was able to partially adopt our own customized authentication flow with Authorizer because they provide flexible enough libs and APIs. I would not be able to fine other product that can handle this easily. Truly, all in one solution ever. ”
Authorizer Save Abandoned
Authorizer is a Password Manager for Android. It emulates an HID keyboard over USB and enters your credentials on your target device. Additionally it supports OTP :key::mobile_phone_off:
- Overview
- Versions
- Reviews
- Resources
Authorizer
Transform Android devices into secure, offline password managers with USB/Bluetooth Auto-Type, OTP, and FIDO support.

Use your Android device as a dedicated hardware password manager. It avoids manual typing of lengthy and complicated passwords by offering USB and Bluetooth Auto-Type features. Acting as a keyboard, Authorizer enables users to automatically input passwords on their PC, laptop, tablet, or another smartphone with a simple in-app button press.
By having your Authorizer-device offline using airplane mode, you create a physical separation between your credentials and the devices commonly used for daily activities. Similar to Security Keys but with enhanced functionality and comfort. This concept helps reduce the likelihood of password breaches and unauthorized access, ensuring stored credentials remain secure from online threats and unrelated apps.
Even if you don’t fully trust the Authorizer app, you can maintain security as long as your Authorizer-device’s underlying OS provides network isolation and data encryption.
Table of Contents

- Features
- Getting started
- Device Recommendation
- Requirements
- Compatibility
Features
- Auto-Type over USB
- Auto-Type over Bluetooth
- Auto-type keyboard layouts for English, German, French, Apple and Neo 2
- Bluetooth FIDO U2F & WebAuthn integration
- OTP integration (TOTP/HOTP)
- Asymmetric encrypted offline backup
- Auto-type keyboard-«commands» like TAB or ENTER for Username and Password fields
- Predefined usernames with placeholders for fast record creation
- Tree list
- Icons
- pwsafe3 file compatible (*)
- Yubikey support (*)
- Biometric protection of your file password (*)
- Time-based file-close (*)
- Screen off can trigger file-close (*)
- Read-only file mode (*)
- Record protection (*)
- Local file backup (*)
- Password expirations (*)
- Password Policies (*)
- Password History (*)
- Notes (*)
- Groups (*)
- Shortcut & alias records (*)
- Home screen widgets (*)
- Powerful Search (*)
- Light & Dark mode (*)
* As Authorizer has its foundation in PasswdSafe for Android, it has also adopted these features.
Getting started
Device Recommendation
For security and privacy reasons, the recommended device is any maintained Google Pixel with GrapheneOS.
Other devices might work as well. But as a lot of smartphone vendors are not publishing its underyling kernel and Android source, they can’t be recommended.Requirements
Authorizer can run on every Android device with version 5 or higher (Lollipop: API/SDK level 21).
For Bluetooth features, minimum version 9 is required (Pie: API/SDK level 28). Higher is recommended for stability reasons.For Auto-Type over USB, low-level root permissions are required to run USB Gadget Tool.
Authorizer does not require root permissions when it is allowed to write to /dev/hidg1 natively (file permissions and selinux needs to be configured for this).Compatibility
Features Windows Linux MacOS iOS Android AutoType — USB X X X X X AutoType — Bluetooth X X X X X FIDO U2F X X X FIDO WebAuthn X X X Features in Detail
Auto-Type over USB and Bluetooth
Authorizer is able to pretend to be an HID Keyboard so it can auto-type the credentials over USB and Bluetooth.
There are Auto-Type buttons at the password entry view. If a button is pressed longer, a different keyboard layout can be choosen. Additional, there is a USB Quick Auto-Type button in the TreeView which auto-types the respective password on a long press.
There are different settings per password entry like delimiter and the password return suffix. In the general App preferences a default keyboard layout can be choosen.Auto-Type over USB requires support of the USB HID device role. This can be enabled with my USB Gadget Tool.
Auto-Type over Bluetooth is currently an experimental feature and only available on Android Pie (9.0) or higher.
Asymmetric encrypted backup on USB mass storage
The concept behind Authorizer is to have an offline device. As a consequence, it can’t create password file backups over the network. To create backups in a comfortable way, Authorizer will open a backup dialog if it detects a new connected mass-storage (e.g. an USB stick connected over an USB On-The-Go adapter). By pressing «Backup now» in this dialog, a backup folder can be selected. It must contain a GPG public key with the file name «pubkey.asc». The default password file will be encrypted with this GPG key and stored in the selected folder.
This feature can be enabled over the general App preference «Enable GPG backup on USB storage».OTP integration
Besides standard username & password entries, Authorizer also supports two-factor authentication (2FA) over one-time passwords (OTP). Time-based (TOTP) and HMAC-based (HOTP) one-time passwords are supported.
The OTP secret can be added to a password entry manually or by scanning a QR code. Afterwards, a press on the empty token field («——«) will generate a new OTP. It is also possible, to auto-type the OTP over USB or Bluetooth by addingas a placeholder directly in the username or password, e.g. in the password «myPa$sword » will be replaced with a newly generated OTP.
Like username, password and other data, the OTP secret is stored in the password file.Additional Auto-Type placeholders
In addition to the
placeholder, Authorizer also supports and for the tabulator and return key. Adding these to the username and/or password will result in auto-typing the respective key (tab or return) instead of the placeholder.
Example: if «peter» is set as the username, «peter» followed by the tabulator key and a newly generated OTP will be auto-typed. Roadmap
Limitations and Known Issues
- When Authorizer creates or modifies psafe3 files, it will add extra fields like auto-type settings, FIDO keys, and icons, which may not be displayed when using other software that supports psafe3.
- Running Authorizer app on tablets is currently not tested.
- The experience of Bluetooth-stack stability can differ between devices, as it is dependent on both the Android version and the specific device being used.
- Due to limitations in the Bluetooth-stack, Authorizer can only be paired as Keyboard OR as FIDO Security key and not both.
- It is important to unpair from the other device as well to prevent unexpected behavior, when establishing a new pairing under a separate profile (like Keyboard or FIDO).
- FIDO U2F & WebAuthn is currently not compatible with Apple MacOS and Apple iOS, as they expecting a different HID_REPORT_SIZE.
- Currently, FIDO credentials can’t be added to existing records.
Contributions & Community
Contributions are highly welcome.
For contributions, discussions and questions around Authorizer, feel free to- Create an issue
- Create a discussion discussion
Please note that I am not interested in further localization of Authorizer, except for auto-type keyboard layouts.
Special Thanks
Authorizer is based on
- PasswdSafe a Password Safe port for Android
- FreeOTP
- WioKey
- and many further
Privacy Policy
Authorizer does not collect any data from your mobile device.
- Camera access is used only for scanning OTP QR codes.
- Location access only used for Bluetooth device scanning and it is optional.
If you believe this policy has been violated in any way, please file an issue.
Authorizer
Authorizer restricts access to a WordPress site to specific users, typically students enrolled in a university course. It maintains a list of approved users that you can edit to determine who has access. It also replaces the default WordPress login/authorization system with one relying on an external server, such as Google, CAS, LDAP, or an OAuth2 provider. Finally, Authorizer lets you limit invalid login attempts to prevent bots from compromising your users’ accounts.
View or contribute to the plugin source on GitHub: https://github.com/uhm-coe/authorizer
Authorizer requires the following:
- CAS server (2.x, 3.x, 4.x, or 5.x) or LDAP server (plugin needs the URL)
- PHP extensions: php-ldap, php-curl, php-dom
Authorizer provides the following options:
- Authentication: WordPress accounts; Google accounts; CAS accounts; LDAP accounts; OAuth2 accounts
- Login Access: All authenticated users (all local and all external can log in); Only specific users (all local and approved external users can log in)
- View Access: Everyone (open access); Only logged in users
- Limit Login Attempts: Progressively increase the amount of time required between invalid login attempts.
- Shortcode: Use the [authorizer_login_form] shortcode to embed a wp_login_form() outside of wp-login.php.
Скриншоты
Установка
- Upload the authorizer directory to the /wp-content/plugins/ directory
- Активируйте плагин используя меню ‘Плагины’ в WordPress
- Specify your server details in the ‘Settings’ menu in WordPress
Часто задаваемые вопросы
Help! I’ve disabled WordPress logins, my external logins (Google/CAS/LDAP/OAuth2) aren’t working, and now I can’t get back in!
If you add external=wordpress to the wp-login.php URL querystring, you can always get the WordPress login form to reappear. For example, if your site is at https://www.example.com, then the URL would be: https://www.example.com/wp-login.php?external=wordpress
Where is this plugin used?
The University of Hawai’i, which provides authentication for student, faculty, and staff members via a centralized service (CAS or LDAP).
Отзывы
Brilliant plugin & team behind it!
Sencillo y práctico
Great plugin
block internal authentication
Create LDAP User/User Registrations
Участники и разработчики
«Authorizer» — проект с открытым исходным кодом. В развитие плагина внесли свой вклад следующие участники:
- Paul Ryan
- the_elusive
- pkarjala
- sky
- Eduardo Larequi
- jojaba
- Anil Natha
Заинтересованы в разработке?
Журнал изменений
- Compatibility fix for Oxygen Builder.
- Update helper text for the LDAP STARTTLS option. Props @TuringTux for the pull request!
- Update French translations. Props @julienlusson!
- Update composer dependencies (phpseclib/phpseclib 3.0.18 => 3.0.19; psr/http-message 1.0.1 => 1.1; psr/http-factory 1.0.1 => 1.0.2; guzzlehttp/psr7 2.4.3 => 2.5.0; apereo/phpcas 1.6.0 => 1.6.1; firebase/php-jwt v6.3.2 => v6.4.0; google/apiclient v2.13.0 => v2.13.2; google/apiclient-services v0.285.0 => v0.297.0; google/auth v1.25.0 => v1.26.0; guzzlehttp/guzzle 7.5.0 => 7.5.1; league/oauth2-client 2.6.1 => 2.7.0; monolog/monolog 2.8.0 => 2.9.1; psr/http-client 1.0.1 => 1.0.2).
- Fix: Remove private pages from search results and archives if visitor is an anonymous user and site is configured to only allow logged in users to see the site. Props @ramrajone for the bug report!
- Fix: Allow minor clock drift (30s) between the WordPress server and Google’s server when processing Google logins.
- Tested up to WordPress 6.2.
- Performance tweaks during Authorizer updates on large multisites.
- Ensure lockout values are integers for invalid login attempts (php8 compatibility).
- Check for existence of super admin roles before adding super admin to approved list on multisite activation.
- Update French translations. Props @julienlusson!
- Allow defining LDAP Directory User and Password via filters ( authorizer_ldap_user and authorizer_ldap_password ) or wp-config.php constants ( define( ‘AUTHORIZER_LDAP_USER’, ‘. ‘ ); and define( ‘AUTHORIZER_LDAP_PASSWORD’, ‘. ‘ ); ) to support integrations with third-party secrets managers (or simply to keep the secrets out of the WordPress database).
- Allow authorizer_custom_role filter on admin logins.
- Allow defining Google Client Secret and OAuth2 Client Secret via filters ( authorizer_google_client_secret and authorizer_oauth2_client_secret ) or wp-config.php constants ( define( ‘AUTHORIZER_GOOGLE_CLIENT_SECRET’, ‘. ‘ ); and define( ‘AUTHORIZER_OAUTH2_CLIENT_SECRET’, ‘. ‘ ); ) to support integrations with third-party secrets managers (or simply to keep the secrets out of the database in plaintext).
- Handle arrays in CAS attribute for first/last name.
- Fix: conflict with W3 Total Cache (when using Azure CDN provider that uses an older guzzlehttp library). Check status
- Fix: only clean up Google session on logout if it exists.
- Fix: Remove all plugin options in database upon deletion/uninstall.
- Fix: Handle Google login error triggered when a stale browser window sends a login request.
- Upgrade composer dependencies (firebase/php-jwt v6.3.1 => v6.3.2, google/apiclient v2.12.6 => v2.13.0, google/apiclient-services v0.272.1 => v0.285.0, google/auth v1.23.1 => v1.25.0, phpseclib/phpseclib 3.0.17 => 3.0.18).
- Mention OAuth2 support in readme.txt.
- Update translatable strings.
- Security: update to phpCAS 1.6.0 to address CVE-2022-39369.
- Update composer dependencies (google/apiclient-services 0.271.0 => 0.272.1; google/auth 1.23.0 => 1.23.1; firebase/php-jwt 6.3.0 => 6.3.1; guzzlehttp/psr7 2.4.1 => 2.4.3; phpseclib/phpseclib 3.0.16 => 3.0.17).
- Fix CAS logouts on proxied CAS servers.
- Set default values for missed multisite option ldap_test_user.
- Respect redirect_to param to wp-login.php with Azure logins. Props @manakuke for discovering the issue!
- Migrate Google Sign-In to Google Identity Services library. Details here.
- Fix inconsistent labels by network users in the approved list (WordPress multisite).
- Update composer dependencies (google/apiclient-services v0.269.0 => v0.271.0).
- Update French translations. Props @julienlusson!
- Fix password reset for WordPress users when «Immediately redirect to CAS login form.» Props @pkarjala for the fix!
- Upgrade composer dependencies (firebase/php-jwt 5.5.1 => 6.3.0; google/apiclient-services v0.254.0 => v0.269.0; google/auth v1.21.1 => v1.23.0; guzzlehttp/guzzle 7.4.5 => 7.5.0; guzzlehttp/promises 1.5.1 => 1.5.2; guzzlehttp/psr7 2.4.0 => 2.4.1; monolog/monolog 2.7.0 => 2.8.0; phpseclib/phpseclib 3.0.14 => 3.0.16; symfony/deprecation-contracts 2.5.1 => 2.5.2; thenetworg/oauth2-azure 2.0.1 => v2.1.1).
- Add setting to support CAS servers behind proxies. Props @slyraskal for the pull request!
- Upgrade guzzlehttp from 7.4.2 to 7.4.5.
- Upgrade composer dependencies (apereo/phpcas 1.4.0 => 1.5.0; google/apiclient v2.12.4 => v2.12.6; google/apiclient-services v0.246.0 => v0.254.0; google/auth v1.21.0 => v1.21.1; monolog/monolog 2.5.0 => 2.7.0; paragonie/constant_time_encoding 2.5.0 => 2.6.3).
- Authorizer now requires PHP 7.2 or higher (phpCAS requirement).
- Add multisite option to prevent subsites from overriding multisite settings.
- Allow LDAP bind as user logging in before attempting anonymous bind (by using the [username] wildcard in the LDAP Directory User settings field).
- Add LDAP test connection to Authorizer multisite settings.
- Tested up to WordPress 6.0.
- Update translatable strings.
- Update French translations. Props @julienlusson!
- Attempt LDAP bind as user logging in if directory user credentials not provided or incorrect.
- Fixed logged errors if LDAP search base couldn’t be found (error only shows in LDAP test connection now).
- Fixed LDAP test connection password saved in database.
- Upgrade composer dependencies (google/apiclient v2.12.2 => v2.12.4; google/apiclient-services v0.242.0 => v0.246.0; google/auth v1.19.0 => v1.21.0; monolog/monolog 2.4.0 => 2.5.0).
- Upgrade composer dependencies (firebase/php-jwt v5.4.0 => v5.5.1; google/apiclient v2.11.0 => v2.12.2; google/apiclient-services v0.213.0 => v0.242.0; google/auth v1.18.0 => v1.19.0; guzzlehttp/guzzle 7.3.0 => 7.4.2; guzzlehttp/promises 1.4.1 => 1.5.1; league/oauth2-client 2.6.0 => 2.6.1; monolog/monolog 2.3.4 => 2.4.0; paragonie/constant_time_encoding v2.4.0 => v2.5.0; phpseclib/phpseclib 3.0.10 => 3.0.14).
- Upgrade guzzlehttp/psr7 2.0.0 => 2.2.1 (security).
- Add LDAP connection test feature (under LDAP settings).
- Update translatable strings.
- Update French translations. Props @julienlusson!
- Add settings icon to dashboard widget header.
- Better styling in dashboard widget.
- Remove «Local WordPress user» icon from Approved User list (uninformative).
- Small coding standards fixes.
- Fix PHP warning when anonymous users browse a restricted site.
- Only load authorizer-public.js when necessary (when site is configured so only logged in users can view the site, current user does not have access, and anonymous users should be shown a message). Props @flim0 for the catch!
- Fix generic OAuth2 connector unable to create username from email. Props @abnerjacobsen for the bug report!
- Redirect to home page after logging in if using custom login url via the WPS Hide Login plugin. Props @wixaw for the report.
- Tested up to WordPress 5.8.
- Authorizer now requires PHP 7.2.5 or higher to support its dependencies. See: this and this if you are running an outdated version of PHP.
- Fix for PHP versions below 7.3 ( array_key_last() is not available for older PHP versions and was added in the last update). Props @ianchan-1 for reporting the issue!
- Update dependencies (apereo/phpcas 1.3.9 => 1.4.0; components/jquery 3.5.1 => 3.6.0; firebase/php-jwt v5.3.0 => v5.4.0; google/auth v1.16.0 => v1.18.0; google/apiclient v2.9.2 => v2.11.0; google/apiclient-services v0.201.0 => v0.213.0; google/auth v1.15.1 => v1.17.0; guzzlehttp/guzzle 6.5.5 => 7.3.0; guzzlehttp/psr7 1.8.2 => 2.0.0; monolog/monolog 1.26.1 => 2.3.4; paragonie/random_compat v2.0.20 => v9.99.100; phpseclib/phpseclib 2.0.32 => 3.0.10).
- Add LDAP Search Filter to plugin settings. Props @hbjusa for the pull request!
- Add [authorizer_login_form] shortcode. Props @shredderwoods and @hilfans for the suggestions!
- Fix PHP warnings about uninitialized oauth2_hosteddomain option.
- Update French translations. Props @julienlusson!
- Note: the next minor version of Authorizer, 3.2, will drop support for PHP 5.6 in order to stay current with phpCAS releases, which now require a minimum of PHP 7.0.
- Note: the next minor version of Authorizer, 3.2, will drop support for PHP 5.6 in order to stay current with phpCAS releases, which now require a minimum of PHP 7.0.
- Update phpCAS dependency from 1.3.8 to 1.3.9.
- Allow restricting OAuth2 logins to a specific domain (of the email address of users authenticating).
- Update oauth2-azure dependency from 2.0.0 to 2.0.1.
- Update Google APIs Client Library for PHP dependency from 2.8.3 to 2.9.2.
- Update Google PHP API Client Services dependency from 0.156 to 0.201.0.
- Update dependencies of dependencies (firebase/php-jwt 5.2.0 => 5.3.0; google/auth 1.14.3 => 1.15.1; guzzlehttp/promises 1.4.0 => 1.4.1; guzzlehttp/psr7 1.7.0 => 1.8.2
monolog/monolog 1.26.0 => 1.26.1; paragonie/random_compat 2.0.19 => 2.0.20; phpseclib/phpseclib 2.0.31 => 2.0.32; psr/log 1.1.3 => 1.1.4). - Update translatable strings.
- Sync role to approved list if edited via bulk action on All Users page. Props @lukeislucas for discovering that edge case!
- Remove unused params in sanitize_user_list().
- Update phpseclib 2.0.30 => 2.0.31 (CVE-2021-30130).
- Fix misplaced «This setting is overridden by a multisite option» in subsite settings within a multisite (caused by change in wp-admin core styles).
- Link to appropriate tab in multisite settings when clicking «This setting is overridden by a multisite option.»
- Fix for warnings setting first/last name on new pending user.
- Use standardized WordPress 5.7 admin colors.
- Fix jQuery deprecation notices in WordPress 5.7.
- Tested up to WordPress 5.7.
- Restore PHP 5.6 compatibility.
- Fix REST API access restriction (allow app passwords introduced in WordPress 5.6).
- PHP 8 compatibility.
- Fix warnings about uninitialized oauth2 options.
- Update Google API PHP Client from 2.8.1 to 2.8.3 (composer update google/apiclient).
- Update Google API PHP Client Services from 0.152 to 0.156 (composer update google/apiclient-services).
- Update composer dependencies (monolog 2.1.1 => 2.2.0; phpseclib 2.0.29 => 2.0.30).
- Fix php errors causing authorizer.js and some vendor assets not to load on network admin. Props @julienlusson for finding this bug!
- Add tenant-specific configuration option to Microsoft Azure oauth2 provider.
- Add Microsoft Azure oauth2 provider.
- Updated French translations. Props @julienlusson for the pull request!
- Authenticate with more providers via OAuth2. Let us know if you have any troubles integrating your OAuth2 provider.
- Add filter authorizer_oauth2_generic_authorization_parameters for targeting the specifics of generic oauth2 providers. Provide an array with options, such as array( ‘scope’ => ‘user:email’ ) , to customize your generic oauth2 provider.
- Add filter authorizer_oauth2_generic_authenticated_email for manually inspecting the results returned from the oauth2 provider to find the resource owner’s email to give to WordPress for the authenticated user. Use this for oauth2 providers that release email addresses in nonstandard places.
- Fix first/last names not getting updated for admins on a CAS or LDAP login.
- Fix PHP warning if invalid login attempt settings are empty (also prevent the “Authorizer lockout triggered for 0 seconds on user after the 0th invalid attempt” simple history log message).
- Fix update usermeta button disappearing in Approved Users list after clicking it.
- Fix serialization of usermeta in Approved Users list for unregistered users.
- Remove bootstrap dependency (replace glyphicons with WordPress dashicons).
- Update translatable strings.
- Update phpCAS from 1.3.6 to 1.3.8.
- Update Google API PHP Client from 2.7.1 to 2.8.1.
- Update google-api-php-client from v2.2.4 to v2.7.1. Note: extra Google Services have been removed from the vendor library to support hosts that don’t like the large vendor library (12,659 files were removed). If you have any problems with your Google sign-ins, please downgrade to 2.9.14 and open a support request!
- Add authorizer_additional_ldap_attributes_to_retrieve filter hook to specify an array of other LDAP attributes to fetch. Props @schtiefel for the pull request!
- Fix W3C validator errors related to type=»text/javascript» in script tags.
- Support ACF Select fields with optgroups in custom usermeta list.
- Better row styling on dashboard widget.
- Add option to update first and last names from CAS/LDAP only if they are empty.
- Don’t print Authorizer help items outside of Authorizer Settings page.
- Log a lockout if we hit the configured limit (via Simple History plugin).
- Fix PHP notice when adding a new user via Dashboard > Users > Add New.
- Tested up to WordPress 5.5.1.
- Successfully tested on WordPress 5.4.
- Fix warnings about missing variable after last update.
- Update translations. Props @julienlusson for the pull request!
- Add feature to disable WordPress logins (only allow logins from configured external services).
- Fix for compatibility issue with User Switching plugin introduced in 2.9.11. Props @ocager for the report!
- Fix for Sign in button styling on small screen sizes.
- Fix for CAS logout issue introduced in WordPress 5.3. Props @jespersundstrom for the report!
- Fix for Active Directory LDAP connections using the domain root as the search base. Props @aszele for the report and testing!
- Fix hiding WordPress logins in WordPress 5.3. Props @ubercow for the report!
- Fix Approved User list spacing with multisite and local users.
- Update translations. Props @julienlusson for the pull request!
- Fix for some LDAP URIs failing validation check; this should address some users unable to connect after upgrading to version 2.9.9. Props @MamoulianDelacroix for the report!
- Allow multiple (failover) LDAP hosts. Props @basildane for the suggestion!
- Update translations.
- Allow emails for LDAP logins. Props @jthomae1 for the suggestion!
- Fix for pending users unable to log out of external service.
- Update styles in Authorizer Settings for WordPress 5.3.
- Better styles in Authorizer Settings for mobile screen sizes.
- Failsafe for restricting Google Logins to specific domain(s).
- Fix edge case where another plugin (e.g., Simple Calendar) has already required google-api-php-client v1.
- Use setHostedDomain() included in google-api-php-client v2.
- Move google-api-php-client due to svn delete issues on deploy.
- Update google-api-php-client library to v2.2.4 to fix issues with OAuth calls. Props @sieumeo for notifying us about the change!
- Fix uncaught CAS exception triggering the new Fatal Error Recovery system (email to admins) in WordPress 5.2.
- Fix spacing on Authorizer Settings page.
- Update screenshots.
- Fix for broken translations in 2.9.0. Props @julienlusson for the pull request!
- Updated French translations. Props @julienlusson for the pull request!
- Fix for conflict with other plugins including the Google API PHP Client (e.g., Simple Calendar).
- Major code refactor to make the codebase easier to manage. Authorizer now requires PHP 5.3 or later.
- Fix for edge case with new unapproved users and stale session IDs. Props @vib94 for the pull request!
- Add missing database migration for new option added in last version.
- Allow CAS servers to link to WordPress accounts via username instead of email (less secure, but supports more uncommon server configurations). Props @mrn55 for the suggestion!
- Clarify that new local WordPress users get emailed an activation link, not a password.
- Update French translations. Props @julienlusson for the updates!
- Update translatable strings.
- Use the WordPress certificate bundle at /wp-includes/certificates/ca-bundle.crt instead of our own. Props @julienlusson for leading us there!
- Fix for PHP warning in edge case where user isn’t allowed to log in.
- Fix pager button styles in Approved User list.
- Fix multisite approved users showing on a site with «override multisite options» enabled.
- Fix for Chrome autofilling the new Blocked User field with saved login email.
- Feature: Specify a domain wildcard (e.g., “@example.com”) in the block list to block all emails from that domain. Props @olhirt for the feature request!
- Update phpCAS library from 1.3.5 to 1.3.6. PHP 7.2 users running CAS are now fully supported. Props @julienlusson for the pull request!
- Fix when inviting existing users to a blog in multisite and setting a role with a display name that doesn’t match the role name. Props @julienlusson for finding the bug!
- Fix for using wp-cli to activate the plugin (broke in 2.8.0). Props @timkite for the discovery!
- Fix for network-activating authorizer via wp-cli.
- Revert overly strict querystring sanitization (caused CAS login problems in servers that don’t encode forward slashes as %2F in querystring values). Props @anamba for the report and bug testing!
- Force asset reload (coding standards changed the formatting of a lot of js and css assets).
- Add authorizer_ldap_search_filter filter (for customizing the LDAP search filter to further restrict LDAP logins). Props @jesus33c for the idea!
- Add authorizer_user_register action. Props @pablo-tapia for the suggestion!
- Allow CAS servers behind redirected URLs. Props @cwhunt for the code!
- Check CAS server reachability by testing serviceValidate endpoint. Props @cwhunt for the code!
- Allow «No role for this site» as a default role for new users. Props @julienlusson for the pull request!
- Update French translations. Props @julienlusson for the pull request!
- Update code to follow WordPress coding standards (php, css, js). Props @michaeldfoley for fixing a bug with our overzealous sanitization!
- Update cacert.pem.
- Fix bug with paging on network approved user list.
- Note: this version requires WordPress 4.4 or later.
- Fix Approved User list sort when set to Date approved / Descending (was still showing as ascending).
- Support multiple LDAP search bases. Props @jmutsaerts for the feature request.
- Compatibility fix for PHP < 5.5. Props @klausdk for the report!
- Additional fix for role not getting set when adding an existing user to a site in multisite. Props @julienlusson for the fix!
- Feature: Approve multiple users at once (by pasting their email addresses into the new approved user field, separated by newlines, spaces, commas, or semicolons).
- Feature: Paging, sorting, and searching in the Approved User list for sites with many users (finally!).
- Update LDAP TLS option for clarity. Props @Scriptkiddi for the pull request!
- Support deprecated multisite constant BLOGID_CURRENT_SITE in addition to BLOG_ID_CURRENT_SITE. Props @er2576 for tracking that down!
- Fix for CAS logouts not working in some situations (remove CAS isAuthenticated() check before CAS logout).
- Fix for updating approved list entry when an email address change is made on the WordPress user profile page in a multisite environment.
- Fix for role not getting set when creating and adding a new user to a blog in multisite. Props @julienlusson for the report and @pkarjala for the fix!
- Added ability to disable the dashboard widget (useful on sites with many users until paged user lists are implemented).
- Fix for the multisite option override link always going to the External Services tab.
- Fix for hide/show of Login Access options when certain options are selected.
- Fix for regression showing certain private posts. Props @InvisibleMass for finding the bug!
- Fix for users without the php-mbstring extension installed.
- Update jQuery multi-select plugin from 0.9.8 to 0.9.12.
- Fix for bug in syncing user roles during login. Props @dsusco for the pull request!
- Fix broken logins caused by regression on previous fix for multivalued email attribute
- Fix for issue with incorrect parsing of an array of email addresses to be converted to lowercase.
- Fix for nonce cookie issue on google logins where cookie was being sent after headers, resulting in an error message.
- Fix for issue with case sensitivity checks on user emails affecting role assignments, user deletions, and user updates in Authorizer. All existing uppercase emails in Authorizer will migrate to lowercase as users log in. Thank you again to @mmcglynn for continued extensive help in testing.
- Update CAS server connection check to accept 300 response codes as valid presence of a CAS server. It is the administrator’s duty to ensure that a redirect on their CAS url is acceptable.
- Fix for issue with approved list roles not updating correctly when changed using the authorizer_custom_role hook. Thank you to @mmcglynn for extensive help in testing.
- Fix for issue with removing user’s roles when removing them from a multisite WordPress install.
- Fix for approved list roles not updating if changed on the fly in authorizer_custom_role hook.
- Update phpCAS from 1.3.4 to 1.3.5. See changelog.
- Fix: Remove user’s role when removing them from the approved list. This is a security feature, in case a removed user is presumed deleted from the site. Since Authorizer does not delete users (to avoid the issue of reassigning or deleting that user’s content), removing their role removes all capabilities from the site until they are re-added to the approved list.
- Fix for duplicate users in approved list (users added via authorizer_automatically_approve_login filter were re-added to approved list each time they logged in).
- Move nonce cookie creation to the first time it is needed (for Google logins). Props @emsearcy for the pull request!
- Respect redirect_to param on CAS logout (if param exists). Props @dgoldber for finding that!
- Better detection of fuzzy permalink matches for private pages. Applies if site is restricted but 404 pages are marked as public; if this was the case, anonymous visitors to malformed permalinks (e.g., “example.com/sample page” or “example.com/sample%20page” instead of “example.com/sample-page”) were able to see the restricted page. Props @6hogan for finding that!
- Fix for CAS logins redirecting to the redirect_to param of wp-login.php.
- Fix for redirect after CAS logout on some CAS servers requiring whitelisted services (add a trailing slash to the logout service param).
- Allow multiple whitelisted domains under Google Hosted Domain. Props Michael K. for the suggestion!
- Drop php-mcrypt library dependency (use openssl library instead since mcrypt is deprecated as of PHP 7.1).
- Fix for some CAS servers redirecting to improper WordPress destination. Props @asithade for the pull request!
- Fix for mixed-case LDAP attribute names (first name, last name, email) not being recognized because ldap_get_entries() returns attirbute names in lowercase. Props @yatesconsulting for the report!
- Fix for immediate CAS redirect hook firing after content was sent to browser, triggering a PHP warning if output buffering isn’t enabled on the web server. Props @steven1350 for reporting the bug!
- Fix for LDAP logins failing if the user password contained a single quote, double quote, or a backslash. Props @alxbr for the research!
- Fix for edge case where a network approved user wouldn’t be allowed to visit wp-admin on a site they had not been added to yet.
- Fix for quotation marks in LDAP password causing LDAP bind to fail.
- Fix for issues with marking translated (via WPML) categories public. Props @mafoti for the pull request!
- Fix for placeholder text for plugin option fields being mistaken for actual values. Props @pkarjala for the pull request!
- Fix for blocked flag in usermeta not getting removed when unblocking a user.
- Feature: Add filter to inspect CAS attributes and automatically approve a user based on any values there. Example:
`
/**
- Filter whether to automatically approve the currently logging in user
- based on any of their user attributes.
- @param bool $automatically_approve_login
- Whether to automatically approve the currently logging in user.
- @param array $user_data User data returned from external service.
*/
function approve_all_faculty_logins( $automatically_approve_login, $user_data ) <
// Automatically approve logins for all faculty members.
if (
isset( $user_data[‘cas_attributes’][‘eduPersonAffiliation’] ) &&
‘faculty’ === $user_data[‘cas_attributes’][‘eduPersonAffiliation’]
) <
$automatically_approve_login = true;
>
return $automatically_approve_login;
>
add_filter( ‘authorizer_automatically_approve_login’, ‘approve_all_faculty_logins’, 10, 2 );
`
- Support LDAP URI in hostname field (e.g., ldaps://ldap.example.edu:636). Props @timkite for your contribution!
- Update translatable strings.
- Simplify CAS login routine.
- Fix for mixed line endings in phpCAS library, causing warnings when running PHP Compatibility Checker plugin. Props @wpgirl369/@eshannon3 for the pull request!
- Fix: Never block access to super admins (or admins in single site mode). Props @eizzumdm and @nreljin!
- Add user to network approved list when they are granted super admin privileges on the Edit User screen outside of Authorizer. Remove user from network approved list when this is revoked (and readd them to the approved list on any site they are currently a member of).
- Fix for notification emails sent to all site users if plugin wasn’t correctly activated.
- Handle CAS servers that return an email address in response to phpCAS::getUser()
- Use wp_remote_get() instead of curl to check CAS server availability. php-curl is no longer a dependency.
- Fix for error introduced in last version with cacert.pem updating.
- Use wp_safe_remote_get() instead of file_get_contents() to update cacert.pem. Props @kriswme2!
- Fix error message shown when login form is first shown and LDAP is enabled. Props @akompanas!
- Fix for lengthy timeout if ldap_start_tls() fails when connecting to an LDAP server. Props @TJuberg!
- Fix a bug preventing first-time login of an approved user when a WordPress user already existed with the same username (but a different email address).
- Remove the spinner overlay when logging in via Google (user could accidentally close the Google sign-in popup, and the spinner prevented them from reopening it by clicking on the «Sign In with Google» button).
- Clean up plugin files (rename ‘inc’ directory to ‘vendor’).
- Fix for CAS version option being selectable when it’s been multisite overridden.
- Fix for missing translatable string (anonymous access message in bootstrap dismissible alert).
- Show all roles in all sites on the Approved Users role dropdown in network admin.
- Make sure role is updated on all sites when approving a new multisite user that already exists in WordPress.
- Feature: Add user to authorizer approved list when added from the Users screen.
- Feature: In multisite, add approved user to all approved sites on first login.
- Feature: Sync role and email address in approved list when changed elsewhere.
- Feature: Add super admins to network approved list on plugin activation.
- Feature: Allow «no role for this site» selection for user roles.
- Fix for existing WordPress user logging in: make sure they are in the approved list.
- Fix for local (WordPress) authentication not respecting the blocked list.
- Fix for whitespace and «mailto:» in emails (trim when clicking approve button).
- Fix for external=wordpress safety login not working if option to immediately redirect to CAS is enabled.
- Fix for deprecation warning in WordPress 4.6: wp_get_sites().
- Fix for deprecation warning in WordPress 4.6: wp_new_user_notification().
- Fix for multisite users not being removed from pending lists.
- Improve code efficiency.
- Revert LDAP/CAS email domain guessing logic (some existing users rely on the old method to determine email address domains). If email domain or CAS/LDAP attribute containing email address is not specified in Authorizer options, guess that email domain is the last two components of the CAS/LDAP host when splitting by periods (e.g., authn.example.com would return an email domain of example.com).
- Tested up to WordPress 4.6.1.
- Update cacert.pem file.
- Tested up to WordPress 4.6.
- Feature: Add method for constructing email address for CAS/LDAP servers that don’t return an email attribute. Simply enter @yourdomain.edu into the mail attribute field to have email addresses be constructed as username@yourdomain.edu.
- Fix: Updates to cacerts.pem for CAS servers now works for WordPress installs behind a proxy. Props dchambel! https://github.com/uhm-coe/authorizer/pull/13
- Feature: Allow restricting Google logins to a single Google Apps hosted domain (e.g., mycollege.edu).
- Update google-api-php-client from 1.0.5-beta to 1.1.5.
- Fix for REST API integration: Authorizer will now deny read/view access via the REST API if the site is private and the user is not authenticated. Other REST API access is unaffected by Authorizer, and is managed by the REST API authentication schema (cookie, oauth, or basic authentication). See http://v2.wp-api.org/guide/authentication/ for details.
- Fix: Warn if php_openssl.dll is not installed on Windows servers (cannot update cacert.pem if it’s missing).
- Fix for mcrypt key length error in php 5.6 and higher.
- Fix for broken newlines in notification emails (also update translations).
- Feature: Customize user roles based on CAS or LDAP attributes. Example:
`
/**
- Filter the default role of the currently logging in user based on any of
- their user attributes.
- @param string $default_role Default role of the currently logging in user.
- @param array $user_data User data returned from external service.
*/
function my_authorizer_custom_role( $default_role, $user_data ) <
// Allow library guests to log in via CAS, but only grant them ‘subscriber’ role.
if (
isset( $user_data[‘cas_attributes’][‘eduPersonPrimaryAffiliation’] ) &&
‘library-walk-in’ === $user_data[‘cas_attributes’][‘eduPersonPrimaryAffiliation’]
) <
$default_role = ‘subscriber’;
>
return $default_role;
>
add_filter( ‘authorizer_custom_role’, ‘my_authorizer_custom_role’, 10, 2 );
`
- Updated Spanish translations. Props @elarequi.
- Fix: Include translatable strings found in javascript files.
- Fix: Force lowercase emails from LDAP. Props @akompanas.
- Fix: Set some LDAP defaults likely to be the same on all installs: ldap_port, ldap_attr_username.
- Fix: Construct LDAP default email domain from LDAP search base, not from host (helps to differentiate between subdomain installs and domains with country codes).
- Translations: Props to @elarequi for wrapping text strings in the translation functions and for providing Spanish translations.
- Fichero authorizer.php: Se preparan todas las cadenas necesarias, para hacerlas traducibles.
- Se crea el directorio /languages, con los ficheros de traducción.
Feature: Add filter to inspect CAS attributes and deny access based on any values there. Props @jojaba for the suggestion. Example:
`
/**